
The lab
Here is how PortSwigger describes it
This lab contains a reflected cross-site scripting vulnerability in the search blog functionality. The reflection occurs inside a template string with angle brackets, single, and double quotes HTML encoded, and backticks escaped.
To solve this lab, perform a cross-site scripting attack that calls the alert function inside the template string.
The last few labs were all about clawing our way out of a string the site had escaped, but this one flips the puzzle, the string is sealed from every side, and the trick is that we never needed to leave it in the first place
The idea#
The word that changes everything here is template literal. normal JavaScript string is written with quotes and is nothing but text. template literal is written with backticks instead, and it has one special power, anything you place inside ${ } is run as a live expression and its result is dropped into the string. it is what lets you write something like `total is ${price + tax}` and have the sum appear you can try this by opening developers tool in browser > console
so template literal is not pure text, it has executable slot built right into it. that completely reframes the attack. every other lab needed us to escape the string before we could run code, but if our input lands inside a template literal and the $, { and } are left alone which is the case here we do not have to escape anything
Step 1 - find where the input lands#
to read the reflection clearly i sent the search request to Burp Repeater and searched for logicbreaker then looked at the response
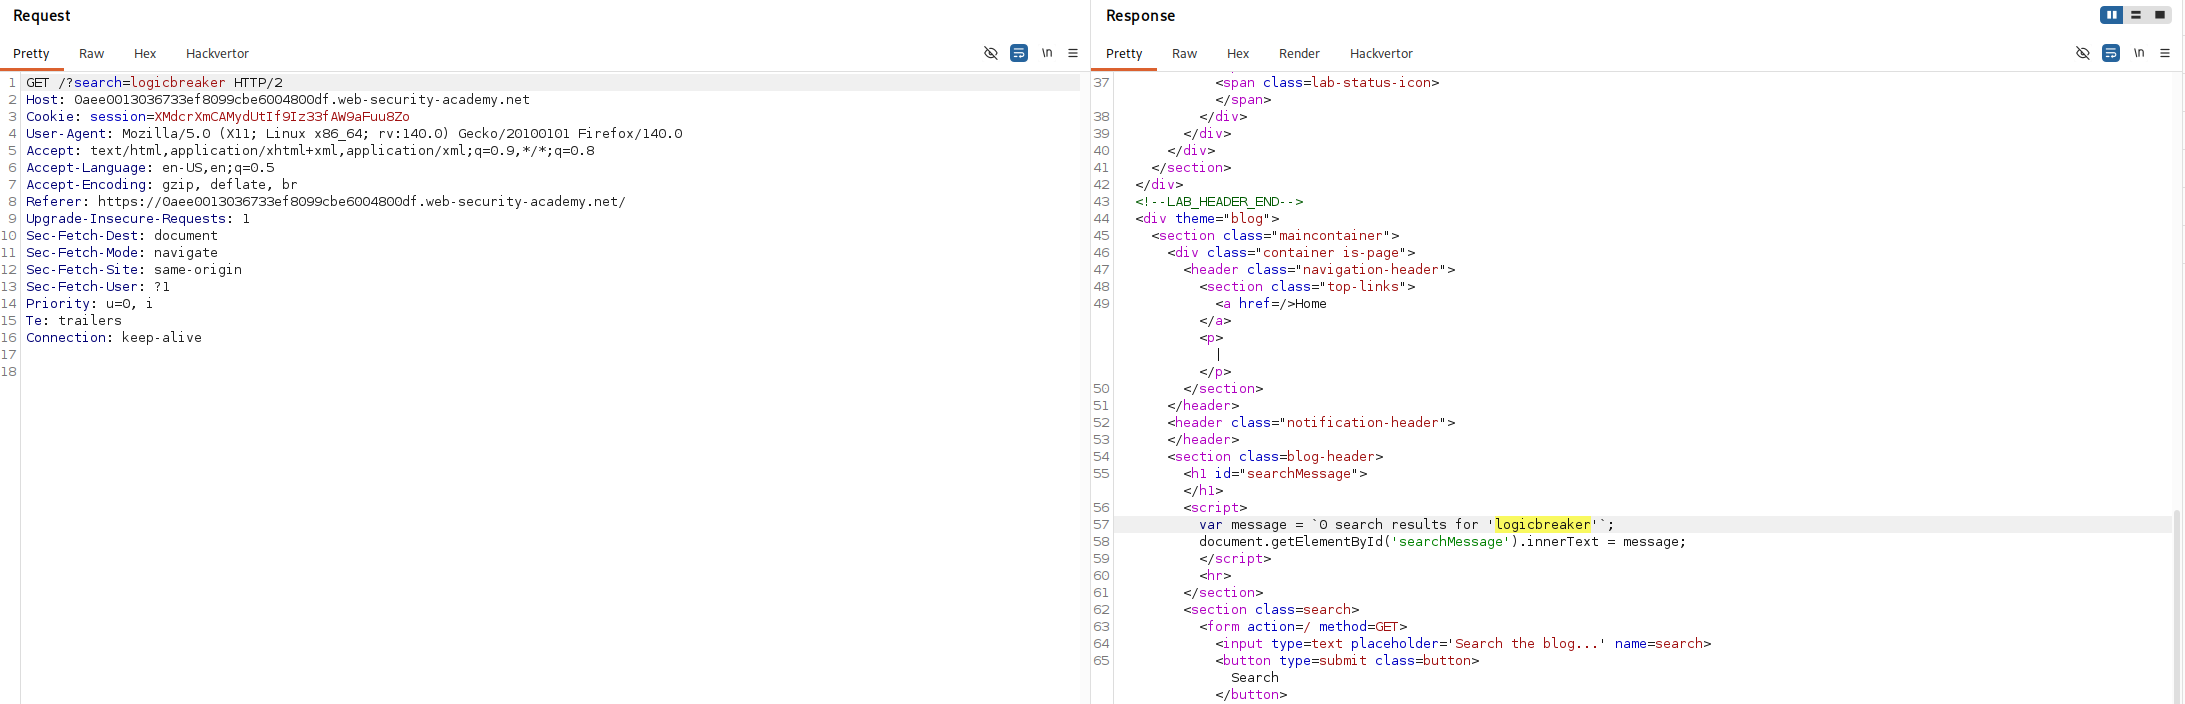
our input comes back inside a script, planted in a template literal, along these lines.
var message = `0 search results for 'logicbreaker'`
backticks around it are the giveaway. this is not an ordinary quoted string, it is a template literal, and that later gets written into the page. so whatever we type is sitting inside a backtick string in live javascript
Step 2 - trying to break out but Failed ;(#
out of habit the first instinct is to break out of the string, so i worked through the usual delimiters one by one. single quote to close the string, the application encodes like \u0027 which is unicode. double quote, same story, angle brackets to start a tag of our own, again both encoded so no tag or script survives :( even a backtick to close the template literal itself comes back
every character that could end the string or open a tag is sanitized properly that's what we see in production applications, if the plan is to get out of this string, there is simply no door left. so the plan has to change
Step 3 - stop escaping and use the template literal itself#
the realisation is that the string we are trapped in is a template literal, and template literal runs whatever sits inside ${ }. the site locked down every quote and bracket that ends the string, but it never touched the dollar sign or the curly braces
${alert(1)}
notice there is not a single quote, backtick, or angle bracket in it, so there is nothing for the filters to catch. when our search term is dropped into the template literal, it becomes roughly `0 search results for '${alert(1)}'`, and the javascript engine does what template literals always do, it evaluates the expression inside the braces so it can splice the result into the string. evaluating alert(1) means calling it, and the alert fires while the message is still being built
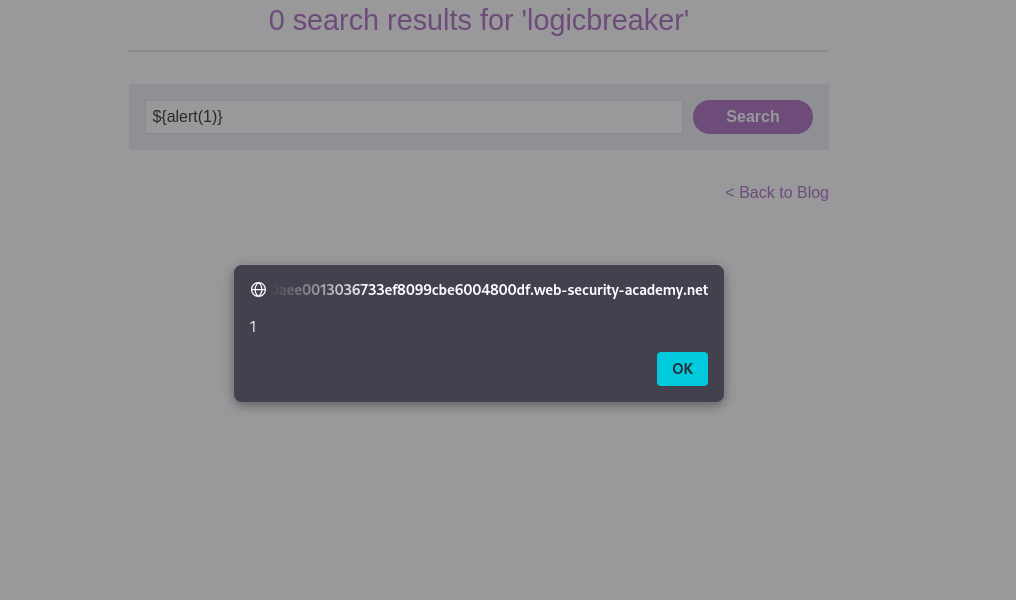
With this, the lab is solved!